Local AI Code Hygiene Audit for Engineering Teams
Evaluates 8 critical risk vectors in under 15 seconds. Score 0–100, offline HTML report, zero data leaves your machine.
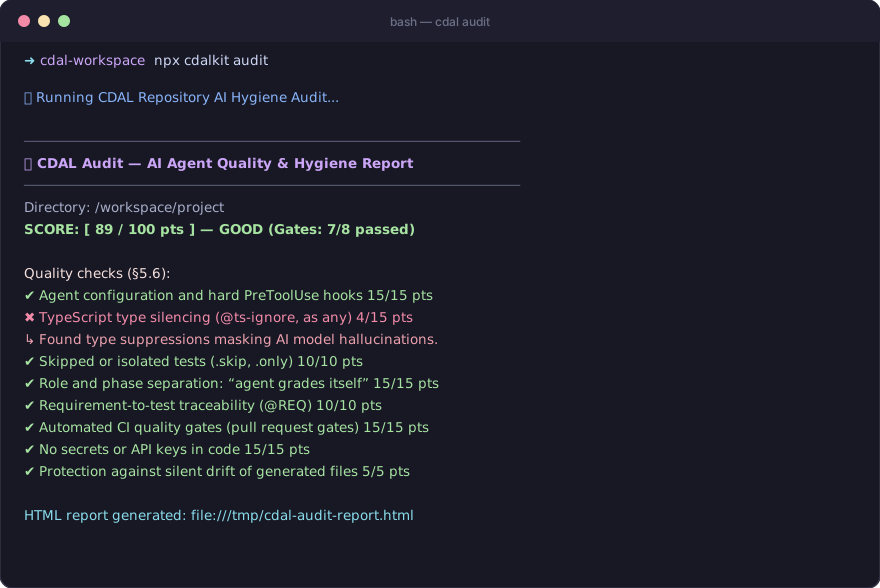
The 8 Checkpoints Evaluated by CDAL Audit
Each check is deterministic, statically evaluated, and calibrated against real-world production repos.
Agent Runtimes & PreToolUse Hooks
Verifies whether role write scopes and blocking PreToolUse hooks are active.
TypeScript Type Silencing Density
Measures density of @ts-ignore, @ts-expect-error, and "as any" per 1k LOC.
Muted or Isolated Tests
Detects tests silenced or isolated by agents (it.skip, describe.only).
Role Separation: "Self-Grading Agent"
Analyzes commits: what % of AI commits touch both tests and production code simultaneously?
Requirements Traceability Matrix
Checks for @REQ: traceability tags linking automated tests to explicit requirements.
Continuous Integration PR Gates
Verifies automated CI workflows enforcing typecheck and testing on pull requests.
Secret Leak Detection
Scans tracked files for exposed private keys, live API tokens, and service credentials.
Generated Code Drift Detection
Detects manual tampering with deterministic generated artifacts and contract bindings.
Fix AI Code Regressions Instantly with CDAL Pro
Did the audit detect test assertions tampering, type muting, or missing gates? CDAL Pro equips you with production-grade kind architectures, 10 agent roles with physical exit 2 test-blocking hooks, and deterministic CI quality gates.
Want to harden your repository immediately?
Check out our 60-second vibecoding manual. Configure rules for Cursor, Windsurf or Antigravity and stop agent regressions.